QUIET · Business & tech
Eight eMudhra intermediate certificate authority keys compromised, blocked by tech firms
AT A GLANCE
- Developments
- 18
- Articles
- 47
- 1 in the last 24 h
- Sources
- 35
- 1 in the last 24 h
- Since
Timeline
Blog post draws lessons from eMudhra on the risks of centralised certificate authorities
Original on tuxmachines.org 1 source
tuxmachines.org
Analysis says eMudhra's exit from SSL/TLS forces customers into a trust migration
Original on biztechweekly.com 1 source
biztechweekly.com
Day-later explainers unpack why eMudhra is leaving the SSL/TLS certificate business
Original on forkast.news 1 source
forkast.news
Oracle joins Chrome in distrusting eMudhra keys; experts urge checks on dependencies beyond browsers
Original on computerworld.com +3 similar4 sources
computerworld.com
3 similar copies from other outlets
Expert blog posts argue the weak keys' impact spreads through unmanaged software trust stores
Original on unmitigatedrisk.com +1 similar1 source
unmitigatedrisk.com
eMudhra's exit from the TLS certificate business draws wider coverage Thursday afternoon
Original on arstechnica.com +2 similar3 sources
arstechnica.com
Coverage two days later recaps Chrome and Firefox blocking keys recovered in seconds
Original on computerworld.com +3 similar4 sources
computerworld.com
1 similar copy from other outlets
eMudhra says it will voluntarily withdraw from the global SSL/TLS certificate business
Original on thenextweb.com +3 similar4 sources
thenextweb.com
2 similar copies from other outlets
eMudhra publicly defends the weak private keys it used to sign certificates
Original on theregister.com 1 source
theregister.com
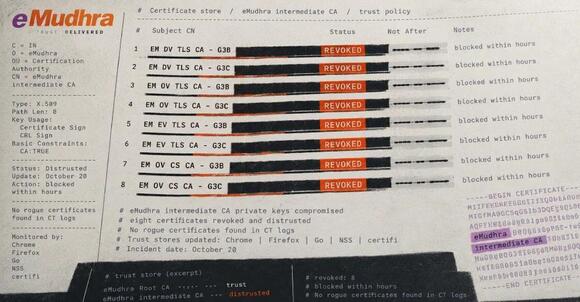
eMudhra revokes the eight intermediate certificates as a cascade of updates follows
Original on cuinfosecurity.com +5 similar6 sources
cuinfosecurity.com
3 similar copies from other outlets
Weak Certificates From Indian CA Cause Cascade of Updates
careersinfosecurity.asia
Weak Certificates From Indian CA Cause Cascade of Updates
inforisktoday.com
Weak Certificates From Indian CA Cause Cascade of Updates
databreachtoday.asia
Fireblocks urges action, warning software outside normal trust stores stays at risk
Original on blockchain.news +1 similar2 sources
blockchain.news
Commentary frames the guessable keys as a web emergency exposing a flawed trust model
Original on techspot.com +3 similar4 sources
techspot.com
1 similar copy from other outlets
CertiK warns crypto trading bots and exchange apps may remain exposed
Original on cointelegraph.com 1 source
cointelegraph.com
Cryptographer warns Mac vulnerability remains despite Apple's certificate block
Original on 9to5mac.com 1 source
9to5mac.com
Next-day reports recap how eMudhra's blunder left CA signing keys exposed to anyone
Original on helpnetsecurity.com +3 similar4 sources
helpnetsecurity.com
3 similar copies from other outlets
Mozilla, Google, Apple Block Eight Weak eMudhra CA Keys
dailysecurityreview.com
Eight eMudhra certificate keys were so weak that one was the number 4
thenextweb.com
Google, Apple, Mozilla rush to block compromised eMudhra certificates
cyberinsider.com
Keys were trivially weak and could be recovered in seconds; one was the number 4
Original on theregister.com +3 similar4 sources
theregister.com
3 similar copies from other outlets
Mozilla and Google confirm eight eMudhra keys compromised; Google, Mozilla, Apple block them
Original on thehackernews.com +2 similar3 sources
thehackernews.com
2 similar copies from other outlets
Go releases emergency update rejecting eight intermediate CA certificates over undisclosed concerns
Original on thehackernews.com 1 source
thehackernews.com
ACTIVITY
18 developments, oldest to newest. Select one to jump to it.
COVERAGE
1 top outlet
Reuters
DETAILS
- Category
- Business & tech · Technology
- Rank in tab
- #15
- Event id
- ev_1GH9jGmu
- Public since
- Timeline
- Editor (LLM), frozen once published